

By Yiddy Lemmer, CEO – CompuConnect, Inc.
Quick answer
Accounting firms can reduce client data exposure when using AI by starting with tasks that need no client information, removing identifying context, approving specific services and accounts, reviewing file permissions and connections, setting conversation retention rules, and training staff. These practices reduce risk but do not guarantee zero exposure.
Use AI Productively While Protecting Client Information
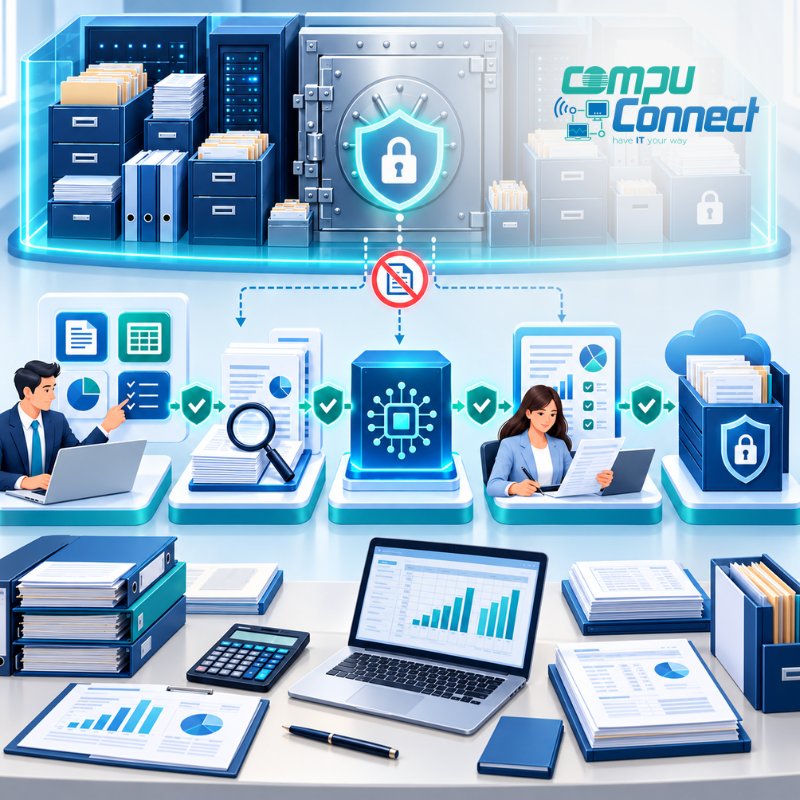
Accounting firms can reduce client data exposure when using AI by starting with tasks that require no confidential information, approving specific services and accounts, reviewing access permissions, and giving employees clear instructions.
The goal is practical: help your team work efficiently while protecting the financial information clients trust you to handle. An office manager drafting a reminder should know what belongs in the prompt. A partner considering a connected assistant should know what needs review before it can access firm records.
These safeguards help reduce risk. They do not guarantee zero exposure.
Before expanding AI use, document:
- Which AI services and accounts employees may use.
- What information they may submit.
- Which files and outside services the assistant may access.
- How conversations and completed work should be handled.
- Who answers questions, approves exceptions, and responds to accidental uploads.
Employees need a process they can follow during a normal workday and under deadline pressure.
What to Evaluate Before Approving AI Use
The practices below address the decisions accounting firm leaders need to make:
- Information needed: Can employees complete the task using a blank template or fictional example?
- Identifiability: Could the remaining details reveal the client, even after names are removed?
- Provider handling: Has the firm reviewed how the specific service handles prompts, uploaded files, and responses?
- Access and connections: Have the relevant accounts, folders, permissions, and outside services been reviewed?
- Everyday use: Are the instructions clear enough for employees to follow and practical enough for managers to maintain?
These practices work together. Apply them according to the task, the information involved, and the firm's approved procedures.
Practical Safeguards for Your Firm's AI Workflows
1. Start with Tasks That Need No Client Data
Who it helps: Employees beginning to use AI and firm leaders deciding which activities to approve first.
What to do: Begin with generic checklists, blank templates, and fictional examples. Use AI to develop the wording or structure, then add client-specific information separately within approved firm systems.
The National Cyber Security Centre advises against including sensitive information in queries to public large language models. This provides a useful starting boundary for public AI use.
Give employees instructions tied to the assignment:
- Describe the result they need.
- Identify the information that must stay out.
- Explain where to complete the client-specific work.
A practical situation: Your office manager needs a missing-document reminder. They could ask:
Draft a brief, professional reminder asking an accounting client to submit outstanding documents. Leave placeholders for the document list and requested delivery date.
They can review the wording and complete the message in the firm's approved system. The client's original email thread does not need to be part of the prompt.
When it does not apply: Some assignments require actual client records. Those need a separate review and approval before employees proceed.
2. Remove Identifying Context Before Submitting a Prompt
Who it helps: Accountants and staff seeking help with formulas, explanations, or client-related scenarios.
What to do: Rebuild the example with fictional names, amounts, dates, and circumstances. Keep the problem you need help solving without reproducing the client's situation.
The Information Commissioner's Office explains that removing direct identifiers alone does not ensure anonymity. Other details, including information combined from different sources, may still identify someone. This guidance supports the identifiability principle discussed here; it is not presented as a U.S. legal requirement.
Before submitting the prompt, ask:
- Does it still describe a recognizable person, firm, or transaction?
- Are distinctive details unnecessary to the question?
- Should the designated reviewer check the example first?
A practical situation: An employee needs help with a spreadsheet formula. They create an invented set of transactions that demonstrates the calculation problem instead of uploading a client ledger.
The prompt focuses on the formula's logic. Client background stays out unless its inclusion has been approved.
When it does not apply: If changing the details makes the question unusable, pause for review. Replacing a name with "Client A" is not enough to establish that the information is anonymous.
3. Approve the Exact AI Service and Account
Who it helps: Managing partners, firm administrators, and office managers responsible for approving AI use.
What to do: Document the specific service, account type, approved activities, and permitted information. Include the provider's training policy, retention arrangements, and contractual protections in the review.
Microsoft's documented commercial Copilot protections state that prompts, responses, and data accessed through Microsoft Graph are not used to train foundation models. Its documentation also explains that interactions are processed and stored. Review both considerations when deciding whether a workflow is appropriate.
Turn that review into straightforward employee instructions:
- Use this approved service and account.
- Use it for these activities.
- Submit only these types of information.
- Contact this person before changing the workflow.
A practical situation: An employee uses an AI assistant personally and wants to use it for client correspondence. Have the firm review the proposed service, account, and activity before they begin.
"Approved for drafting generic reminder templates" gives employees a useful boundary. A broad statement that "AI is approved" leaves too much open to interpretation.
When it does not apply: Service approval does not cover every possible use. Review the workflow again when the task, information, account, or connected services change.
4. Review File Permissions Before Connecting AI
Who it helps: Firms considering AI connected to Microsoft 365 content and managers responsible for access to client records.
What to do: Review the relevant client folders, shared sites, and group memberships before enabling the connected workflow. Confirm that access matches each employee's responsibilities.
Microsoft documents that Copilot can surface organizational information a user already has permission to view. Reviewing those permissions is therefore an important part of preparing for connected AI use.
Keep the review focused on business needs:
- Who needs access to these records?
- What work requires that access?
- Who approves changes?
- Which administrator will implement them?
A practical situation: During preparation, the firm discovers that a general staff group can view a folder intended for partners. Have the responsible manager review that access and the administrator correct it before proceeding.
Give employees a clear contact for unexpected access. They should not have to decide whether information is appropriate to use simply because it appears in a result.
When it does not apply: This step does not apply to a standalone tool with no connection to firm repositories. The firm still needs to review how that tool handles information employees submit directly.
5. Review Web Search and Third-Party Connections Separately
Who it helps: Employees and managers considering assistants that search the web or use additional agents and integrations.
What to do: Identify every connection involved in the proposed assignment. Review web search settings and each additional agent's privacy statement and terms before approving the workflow.
Microsoft explains that Copilot's generated web-search queries can draw on prompts and document content. Its agent guidance separately directs users to review an agent's own privacy statement and terms.
Sources: Microsoft web search and Microsoft agent guidance
Make the decision before assigning the work:
- Does the task require public research?
- Does it require confidential internal information?
- Can those activities be completed separately?
- Have the necessary connections been approved?
A practical situation: A partner wants an assistant to combine a confidential client acquisition memo with public company research. Review the internal-document work and external research separately.
Consider whether the employee can request the public research without including the confidential memo or explaining the client's plans.
When it does not apply: Disabling web search does not complete the review. The core service and any remaining connections still need approval for the intended use.
6. Treat Saved AI Conversations as Sensitive Records
Who it helps: Firm administrators setting handling rules and employees saving or sharing AI-assisted work.
What to do: Establish clear retention and sharing instructions. Before forwarding a response or saving it in a shared folder, review what it contains and who should receive it.
Microsoft documents that Copilot Chat logs prompts and responses, and that available retention controls depend on the subscription.
Include the end of the assignment in the instructions:
- Where should the finished work be saved?
- Who may receive it?
- What rules apply to the conversation history?
- Who handles questions about retention or deletion?
A practical situation: An employee completes an approved client-related assignment and wants to share the conversation as a training example.
Have them prepare a generic version unless sharing the original has been specifically approved. Review the replacement before distributing it, with attention to any client details that remain.
When it does not apply: Retention rules cannot authorize information that should never have been submitted. Report an accidental upload to the designated contact and follow the firm's response instructions.
7. Train Staff on Approved Uses and Protect Their Accounts
Who it helps: Partners, office managers, permanent employees, and seasonal staff.
What to do: Turn the firm's decisions into examples employees recognize. Show what is allowed, what requires approval, and what to do after an accidental upload. Include account protection in those instructions.
IRS guidance recommends employee security education and multifactor authentication. Applying that education to approved AI uses and accidental uploads is the practical recommendation here.
Build the guidance around everyday accounting work:
- Drafting client reminders.
- Getting help with spreadsheet formulas.
- Working with confidential financial records.
- Requesting approval during a deadline.
- Reporting information submitted by mistake.
Ask employees to explain what they would do when an assignment falls outside the approved examples. Use their questions to improve the instructions.
A practical situation: A seasonal employee considers pasting a tax return into an unapproved assistant. The next step should be clear: stop and contact the designated person.
Assign someone to respond so the employee can get a decision and continue working through an approved process.
When it does not apply: Training and account protection do not make an unsuitable service appropriate for confidential information. Firm leaders still need to approve the activities and information involved.
Put an Approved AI Workflow into Practice
Choose an initial task and have someone review the full workflow before expanding AI use:
- Define the assignment: State the intended result and the information needed.
- Set the boundary: Document what employees may submit and what must stay out.
- Confirm responsibility: Name the person who approves the workflow and handles exceptions.
- Complete the instructions: Explain where finished work belongs and how conversations should be handled.
- Walk through an example: Have an employee follow the process and flag unclear decisions.
Your firm should be able to explore AI with clear boundaries around client information and a practical plan your employees can follow. Start with an approved workflow, review the settings and access behind it, and give your team a clear path for questions.
CompuConnect helps CPA and accounting firms protect confidential financial data, keep employees productive, and plan technology changes with confidence. Our proactive IT Support and Cybersecurity Services and 100% live human support give your firm knowledgeable people to turn to as those decisions evolve.
Ready to review how AI fits into your firm's technology and security plans? Schedule a Discovery Call.
Frequently Asked Questions About AI and Client Data
Can our office manager coordinate this without understanding all the technical details?
Yes. The office manager can collect proposed uses, document decisions, and communicate approved instructions.
Assign questions about settings, permissions, and provider handling to the appropriate technical reviewer. Keep approval responsibilities clear so the coordinator knows when to escalate.
What should we do when an employee requests an exception?
Ask them to describe the assignment, proposed service, and information they want to use. Have the responsible person review the request before the employee proceeds.
Document the decision and any conditions so employees have a consistent answer when a similar request comes up.
How should we handle an urgent request during tax season?
Establish the escalation process before deadline pressure builds. Employees should know whom to contact when an assignment falls outside the approved guidance.
Give the designated reviewer responsibility for responding. Urgency should trigger a clear review process rather than leave employees to make an unsupported decision.
What should an employee report after an accidental upload?
Have them promptly contact the designated person and explain:
- Which service and account they used.
- What information they submitted.
- What happened afterward.
Can accounting firms use AI without uploading client information?
Yes. Start with generic email templates, blank checklists, and fictional spreadsheet examples. Ask for help with wording or structure, then add client-specific details separately inside your firm's approved systems.
Is removing a client's name enough to make a prompt anonymous?
No. Other details can still identify someone, especially when combined with additional information. Review the entire scenario and use fictional circumstances where possible. If you cannot confidently remove identifying context, do not submit it.
Does "not used for AI training" mean information is not stored?
No. Microsoft's commercial Copilot documentation describes restrictions on foundation-model training alongside processing and storage of interactions. Review training, retention, and contractual protections separately before approving a service.
What should we check before connecting AI to Microsoft 365?
Review access to client folders, shared sites, and group memberships. Microsoft Copilot can surface organizational information the user already has permission to view. Also review the proposed workflow's web search settings and any additional agents or integrations.
What should employees do if they accidentally upload confidential client information?
Contact the firm's designated person promptly. Explain which service was used, what information was submitted, and what happened afterward. Follow the firm's approved response instructions rather than improvising a cleanup process.
Follow the firm's approved response instructions. This article does not provide a service-specific incident procedure.
Last reviewed: October 2026
About the Author
 Yiddy Lemmer is the Founder and CEO of CompuConnect IT, a leading IT support and cybersecurity firm serving small and midsize businesses across New York and New Jersey. With over 18 years of hands-on experience, multiple Microsoft and CompTIA certifications, and deep roots in Brooklyn, Yiddy leads with a passion for technology, service excellence, and helping businesses thrive through secure and efficient IT systems.