

By Yiddy Lemmer, CEO – CompuConnect, Inc.
After discovering a data breach, businesses should immediately activate their incident response plan, contain unauthorized access, preserve evidence, and involve their IT security team, legal counsel, and cyber insurance provider. Next, determine what information was affected, meet applicable notification requirements, and restore operations safely.
The priority is to protect people and keep the business operating while establishing what happened. A password reset or successful backup restoration alone does not complete a data breach response.
For small and midsize businesses in Brooklyn, Manhattan, New York City, Brick, South Jersey, and the Tri-State Area, a documented response gives leadership a practical way to coordinate decisions, communications, and recovery.
What should a business do first after a data breach?
1. Activate the response team and contain the incident
Assign an incident lead. Involve your managed services provider (MSP), cybersecurity specialists, legal counsel, and business leadership. Notify your cyber insurer promptly and check policy requirements for response providers and expenses.
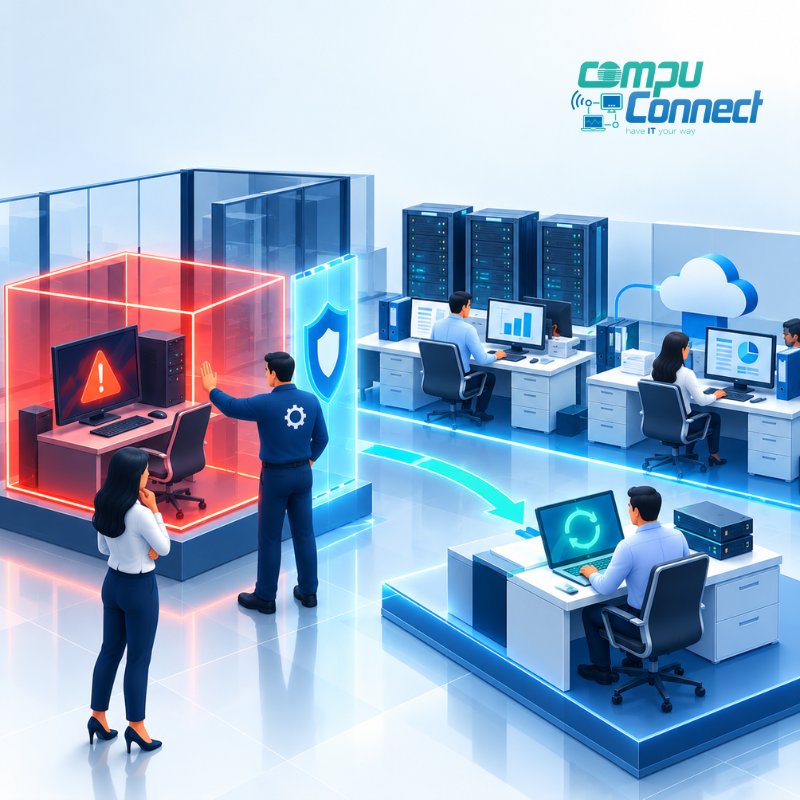
Have responders isolate affected devices or restrict compromised accounts to stop further unauthorized access. Avoid wiping, reinstalling, or routinely shutting down affected computers before forensic guidance. The Federal Trade Commission (FTC) recommends taking affected equipment offline while preserving evidence and involving appropriate experts. [Source]
Use a trusted communication channel if company email may be compromised. Give employees one reporting contact and clear instructions about affected systems.
2. Preserve evidence and establish the facts
Ask qualified responders to preserve relevant logs, suspicious messages, and system evidence. Maintain a timeline of discovery, actions, and decisions.
Determine:
- Which devices, accounts, cloud services, and vendors were involved?
- What information was accessed, exposed, or taken?
- Which people and business processes may be affected?
- Does unauthorized access remain possible?
The FTC advises businesses to document their investigation and preserve forensic evidence. [Source]
Keep confirmed facts separate from assumptions. A useful leadership update states what is known, what remains uncertain, and who owns the next decision.
Is changing passwords enough after a business email compromise?
No. A compromised Microsoft 365 account requires investigation beyond a password change. Microsoft's guidance includes disabling the affected account during investigation, revoking sessions, reviewing authentication methods and application permissions, and checking for unauthorized forwarding and inbox rules. [Source]
For business leaders, the practical questions are straightforward: Has the attacker's access been addressed? Were other accounts affected? Were fraudulent messages sent to clients or vendors?
For example, if an employee's mailbox sent altered payment instructions, assign someone to coordinate direct verification with affected contacts through a trusted channel. Preserve the messages for investigators.
Who must businesses notify after a data breach?
Notification depends on the information involved, affected individuals, applicable laws, contracts, and industry requirements. Have legal counsel identify recipients, deadlines, and required notice content early. The FTC specifically recommends reviewing applicable state and federal requirements. [Source]
There is no single notification deadline that applies to every business data breach. These examples illustrate why the response must be tailored:
| Requirement | What leadership should know |
|---|---|
| New York breach notification law | Where applicable, notice to affected residents must be made as expediently as possible, without unreasonable delay, and within 30 days after discovery, subject to statutory provisions, including qualifying law enforcement delays. [Source] |
| New Jersey breach notification | For breaches requiring customer notification, the New Jersey State Police says businesses must report the breach to the Division of State Police before notifying customers. [Source] |
| FTC Safeguards Rule | Covered financial institutions must report qualifying notification events involving at least 500 consumers' unencrypted customer information to the FTC as soon as possible and within 30 days of discovery. [Source] |
| HIPAA Breach Notification Rule | Following a breach of unsecured protected health information, covered entities generally must notify affected individuals without unreasonable delay and within 60 days of discovery. HHS reporting and possible media notice have additional requirements. [Source] |
These examples are not a complete compliance checklist. Counsel should evaluate exceptions, state agency notices, contracts, and overlapping obligations. A maximum deadline is not a recommended waiting period.
What should CPA and accounting firms do?
CPA and accounting firms handling tax preparation data should promptly involve their security team and counsel. The IRS directs tax professionals to report client data theft to their local IRS stakeholder liaison so the agency can act against fraudulent returns. [Source]
Tax preparation firms are among the businesses the FTC identifies as potentially covered by the Safeguards Rule. Its notification-event definition includes encrypted customer information when the encryption key was accessed by an unauthorized person. [Source]
What should home healthcare agencies do?
Home healthcare agencies should assess whether compromised office email, billing platforms, administrative systems, or shared files contained protected health information. Where HIPAA applies, leadership should involve its privacy and security officials to assess the incident and coordinate required notices. HHS distinguishes covered-entity notification duties from business-associate duties. [Source]
How can businesses restore operations safely?
Business continuity and disaster recovery should follow a controlled sequence. Establish which workflows must return first, who approves restoration, and how staff will work during the outage.
Have the recovery team validate backups and address the compromise before reconnecting affected systems. Restoring files without resolving the underlying access problem can leave the business exposed again.
The Canadian Centre for Cyber Security recommends tested recovery plans and protected backups as part of ransomware preparedness and recovery. [Source]
Useful recovery acceptance criteria include:
- Essential applications and records are available to authorized staff.
- Restored systems have passed the response team's security checks.
- Temporary access and workarounds have an owner and removal date.
- Monitoring is in place to identify renewed suspicious activity.
Backup recovery restores availability. It cannot undo information already disclosed, so investigation and notification work may continue after systems return.
What should change after the incident?
Turn the findings into an improvement plan with named owners and deadlines. Depending on the cause, priorities may include phishing-resistant multifactor authentication (MFA), tighter administrative access, patch management, network segmentation, protected backups, and employee security training. These are among the preventive measures recommended by the Canadian Centre for Cyber Security. [Source]
For leadership, request evidence of progress: a completed access review, a successful recovery exercise, or a tested incident response contact list. A recommendation becomes useful when someone is accountable for completing it.
Proactive managed IT services should connect those improvements to daily operations, budget planning, and business continuity.
Frequently asked questions about business data breaches
Does a small business need a data breach response plan?
Yes. A practical plan identifies decision-makers, response contacts, communication methods, and recovery priorities. Keep a copy accessible if normal systems are unavailable. The Canadian Centre for Cyber Security recommends offline access to incident response plans. [Source]
Can a business wait until the investigation is finished to consider notification?
Do working backups mean the breach is resolved?
No. Backups help recover operations, but they do not establish what information was exposed or whether unauthorized access has been removed. Recovery, investigation, and notification are separate workstreams.
Build a clearer response with CompuConnect
Your business needs dependable systems and people who can explain the next step. CompuConnect combines proactive managed IT services, business cybersecurity, strategic IT planning, and 100% live human support to help leadership plan for stability and business continuity.
For organizations seeking business IT support in Brooklyn, Manhattan, NYC, Brick, South Jersey, and the Tri-State Area, start with a review of your incident response plan, access controls, and backup recovery readiness.
Schedule a Discovery Call with CompuConnect to discuss your cybersecurity and business continuity planning.
About the Author
 Yiddy Lemmer is the Founder and CEO of CompuConnect IT, a leading IT support and cybersecurity firm serving small and midsize businesses across New York and New Jersey. With over 18 years of hands-on experience, multiple Microsoft and CompTIA certifications, and deep roots in Brooklyn, Yiddy leads with a passion for technology, service excellence, and helping businesses thrive through secure and efficient IT systems.